Oct. 1, 2026
Local LLMs Support Human Pentesters
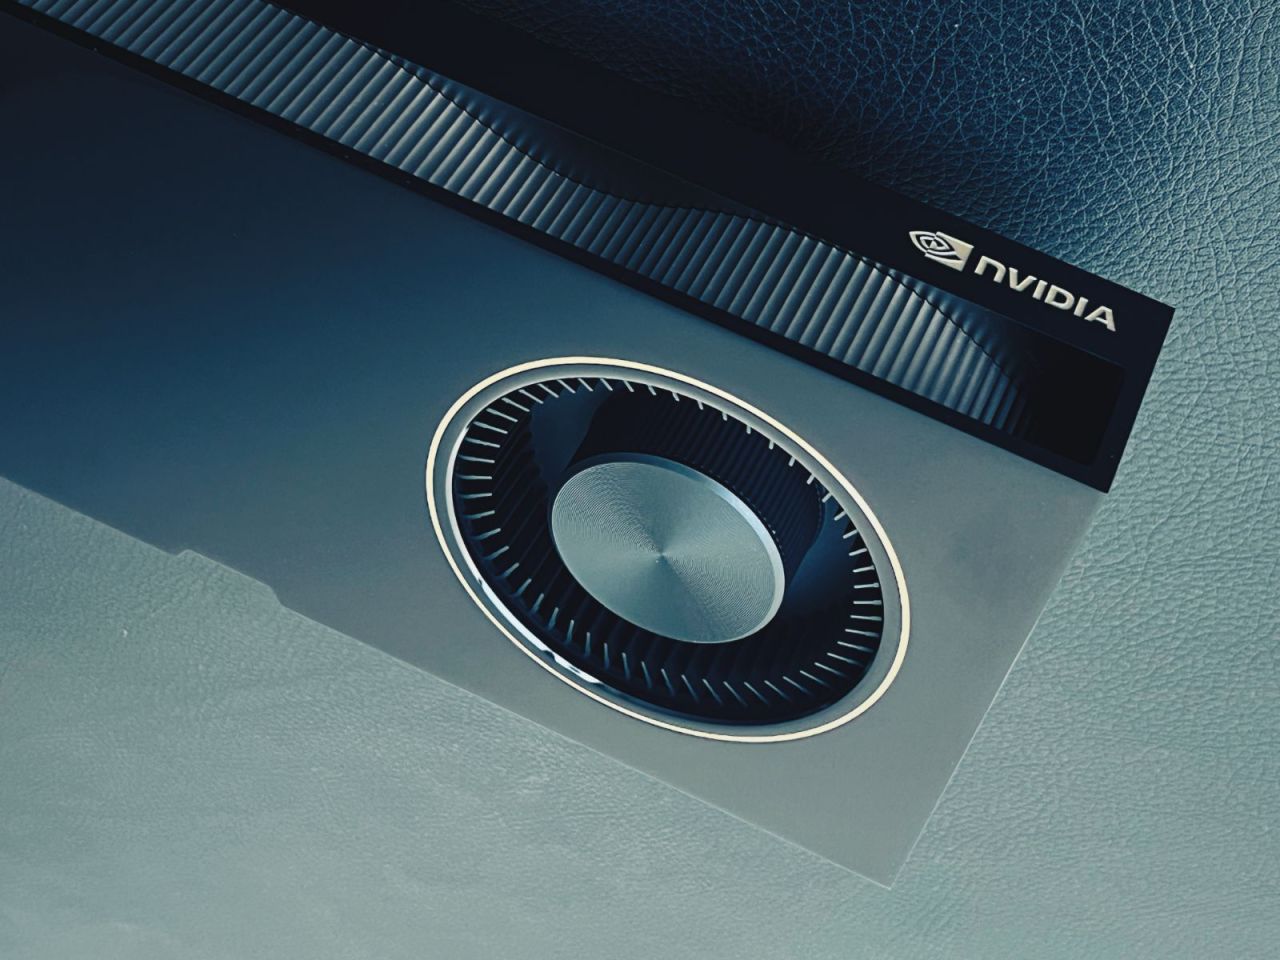
The binsec GmbH is equipping its pentest team with NVIDIA RTX PRO 6000 Blackwell graphics cards. On these professional workstation GPUs, the company runs abliterated Qwen models locally to support human, manual penetration testing. The language models act as assistants for our testers: they support information analysis, script and exploit development, and the documentation of findings – while the human pentester remains fully in control of the testing process.
Abliterated Models for Technical Workloads
Abliteration is a method that removes the refusal direction from a large language model. The result is a model that no longer falls back on safety responses, but executes technical instructions reliably. For penetration testing, this matters whenever the model supports a tester directly – for example when analysing suspicious configurations, interpreting attacker behaviour, or generating and reviewing test scripts and exploit code: the model should be an assistant, not a gatekeeper.
The Qwen model family from Alibaba is available in various sizes with open weights. The abliterated variants are run exclusively on binsec's own hardware and are not reachable from the internet.
No Test Data Leaves the Company
Penetration testing generates highly sensitive data: network topologies, credentials, source code and findings. With commercial LLM services, such data would be processed by third parties. By running the models on its own RTX PRO 6000 Blackwell cards, the binsec GmbH keeps all data on its own premises – without any public cloud connection or external platform dependency.
This is consistent with binsec's self-operated infrastructure concept: dedicated networks, dedicated service infrastructure and now dedicated AI infrastructure for the support of manual penetration testing.

Talk now
to our
Pentest experts.
Contact us
OSCP, M.Sc. Security Management
Talk now to our Pentest experts.
OSCP, M.Sc. Security Management
Manual Penetration Testing by Certified, In-House Senior Penetration Testers
Who tests
For more than ten years, binsec has stood for technically rigorous, strictly manual penetration testing. All engagements are conducted exclusively by employed senior penetration testers. Freelancers or subcontractors are not involved. Our clients work directly with the responsible senior tester who personally performs and technically leads the assessment. Communication is conducted in German and English; international projects are a regular part of our work. Our experts hold recognized offensive security certifications such as OSCP, OSCE, CRTO, and BACPP.
What we test
Our project experience covers complex enterprise networks, modern web and API architectures, and hybrid infrastructures. We work with organizations in manufacturing and industry, financial services and insurance, healthcare, IT and software providers, as well as public institutions. Technical, regulatory, and organizational requirements are systematically taken into account.
How we work
Our tests are based on a structured and reproducible methodology. They align with established standards such as OWASP and OSSTMM and are adapted to the specific project scope. Each assessment follows clearly defined phases: structured reconnaissance, manual analysis, targeted exploitation, and validated impact assessment. Automated tools support the process; identification, verification, and evaluation of vulnerabilities are performed manually.
Where we operate and document
Assessments are not conducted from cloud infrastructures. We operate our own infrastructure in a data center in Frankfurt. From there, all engagements are centrally executed and documented within our internal system PTDoc. The AI support for our testers also runs without cloud services: local LLMs (abliterated Qwen models) work on NVIDIA RTX PRO 6000 Blackwell GPUs in our data centers in Germany. PTDoc serves as the central documentation platform for all project data, evidence, and evaluations. All findings are recorded in a structured manner, technically described, risk-assessed, and supported by reproducible proof-of-concept information.
What you receive
We identify technical vulnerabilities and assess their business impact. Findings are evaluated based on risk or CVSS. The result is a clearly structured report including an executive management summary and detailed technical documentation. Re-testing of identified vulnerabilities is an integral part of our service.


 +49 692475607-0